How much does non-compliant security training cost in fines?
The cost of non-compliance with security awareness training has no fixed fine. See which rules apply, what drives penalties, and what MSPs should document.
DefendWise
DefendWise
There is no universal fine for non-compliant security awareness training in 2026; the financial exposure depends on the applicable law, the organization’s obligations, and the facts of the violation. A training failure can also create remediation costs, contractual disputes, and evidence problems that a headline regulatory penalty does not capture.
TL;DR
- The cost of non-compliance with security awareness training has no universal fine; identify the applicable obligation first.
- GDPR, HIPAA, and the FTC Safeguards Rule impose different duties; a missed course does not determine a penalty.
- PCI DSS requirements and SOC 2 examinations are not interchangeable with statutory fines.
- MSPs should document training coverage, completion, exceptions, and the client’s responsibility for corrective action.
For MSPs evaluating Defend Wise security awareness training, the buying question is not whether software makes fines disappear. It is whether the training service supports the client’s actual obligations without adding seat-count friction.
How much does non-compliant security training cost in fines?
There is no standard fine per untrained employee or missed course. Regulators assess violations under particular laws, not a universal security training tariff. A defensible 2026 assessment starts by identifying which requirements apply and what conduct failed to meet them.
| Requirement | How training fits | Financial consequence to distinguish |
|---|---|---|
| HIPAA Security Rule | Requires a security awareness and training program for the workforce, including management | Civil monetary penalties concern HIPAA violations, not a universal missed-course charge |
| GDPR | Includes staff awareness and training within the data protection officer’s monitoring duties, where applicable | Administrative fines depend on the infringement and the assessment factors in Article 83 |
| FTC Safeguards Rule | Requires security awareness training for personnel at covered financial institutions | Enforcement depends on the violated obligation and available legal authority |
| PCI DSS | Includes security awareness requirements for entities within scope | Payment ecosystem consequences arise through contractual relationships, not a government training fine |
| SOC 2 | Examines controls relevant to the selected trust services criteria | Control exceptions can affect the examination and commercial relationships; SOC 2 does not impose statutory fines |
These are different obligation types. Do not turn a regulator’s maximum penalty, a card-network assessment, and an audit exception into the same cost category. That produces a misleading risk estimate before the training program is even assessed.
Why this matters
Security awareness training is a control, not a fine-avoidance certificate. A completion report establishes that recorded learners completed assigned material; it does not establish that every applicable legal obligation was satisfied.
For an MSP, the practical problem is the gap between delivering training and proving the agreed service was delivered. You need a clear record of who was covered, what was assigned, what remained incomplete, and who owned the follow-up.
A 2026 client review should therefore separate regulatory exposure from delivery obligations. Your service agreement defines what you undertake to do. The client’s applicable laws and contracts define obligations that buying a training platform does not erase.
HIPAA: assess the training program, not just attendance
The HIPAA Security Rule requires a security awareness and training program for the workforce, including management. The relevant provision is 45 CFR 164.308(a)(5), which addresses security reminders, malicious software, log-in monitoring, and password management through its implementation specifications.
That is not the same as a rule that every missed annual course generates a predetermined fine. Evaluate the organization’s program, applicable implementation specifications, documented decisions, and response to identified gaps.
HIPAA also has documentation obligations. Under 45 CFR 164.316(b), required Security Rule documentation must be retained for 6 years from creation or the date when it last was in effect, whichever is later. That requirement does not mean every document in a training platform automatically has the same legal status.
Best for HIPAA program reviews: assess the policy, workforce coverage, delivery records, and corrective actions together. Attendance alone is too narrow; treating every training artifact as legally identical is too broad.
GDPR: training supports accountability, not immunity
GDPR Article 39 identifies awareness-raising and training of staff involved in processing operations among the data protection officer’s compliance-monitoring duties. Article 32 separately addresses security measures appropriate to the risk.
The distinction matters. GDPR does not create a universal annual training fine for every organization, nor does completing a generic course prove that processing activities meet GDPR requirements.
Article 83 requires consideration of factors including the nature, gravity, and duration of an infringement, intentional or negligent conduct, mitigation, and relevant previous infringements. A penalty assessment therefore requires the actual infringement, not merely the number of overdue learners.
Best for GDPR-related reviews: connect training to staff responsibilities and the personal-data risks those responsibilities create. Keep the evidence usable, but do not describe training completion as proof of GDPR compliance.
FTC Safeguards Rule: connect training to the information security program
The FTC Safeguards Rule applies to covered financial institutions under FTC jurisdiction. Its personnel provisions include security awareness training that is updated as necessary to reflect risks identified through the risk assessment.
The rule also addresses qualified information security personnel and keeping those personnel’s knowledge current. A generic employee-awareness course and specialist security training serve different purposes; do not substitute one for the other.
For a 2026 review, ask whether training reflects the organization’s identified risks and whether responsibility for maintaining it is assigned. A static completion report cannot answer those questions by itself.
Best for Safeguards Rule reviews: assess training within the written information security program. The benefit is alignment with identified risks; the limitation is that training cannot replace the program’s other required safeguards.
PCI DSS and SOC 2: separate contractual and assurance exposure
PCI DSS includes security awareness training requirements for personnel upon hire and at least once every 12 months. Its awareness program also needs to address relevant threats and staff responsibilities.
Those requirements do not turn PCI DSS into a government fine schedule. Establish the entity’s scope, applicable validation obligations, and relevant agreements before estimating financial consequences.
SOC 2 is different again. It is an examination of controls against applicable criteria, not a regulator issuing training fines. A training-related control exception requires analysis in the context of the control description, examination period, and auditor’s findings.
Best for client reporting: label the obligation correctly. PCI DSS evidence supports a payment-security requirement; SOC 2 evidence supports an assurance examination. Neither label proves compliance with every law that applies to the client.
Why the cost of non-compliance varies
The cost of non-compliance with security awareness training varies because the underlying obligations and facts vary. Use these factors to scope an assessment rather than multiplying overdue learners by an invented fine.
- Applicable authority: identify the law, contractual requirement, or examination criterion before discussing consequences.
- Nature of the failure: distinguish an isolated incomplete assignment from an absent program or an ignored control weakness.
- Duration and repetition: establish when the issue began, when it was discovered, and whether it recurred.
- Risk and consequences: assess the affected information, relevant threats, and actual consequences under the applicable framework.
- Corrective action: record what changed after discovery, who owned the change, and whether the gap was resolved.
- Evidence quality: preserve records that support the facts rather than relying on an unsupported assurance that training happened.
Not every factor has the same legal weight under every regime. Use the relevant authority’s rules for the legal assessment and the same underlying records for operational follow-up.
How should an MSP document a training gap?
Record the gap before promising the outcome. An MSP needs a defensible service record, while the client needs an accurate account of its remaining obligations.
- Map obligations. Identify the client entity, relevant requirements, covered personnel, and agreed service scope. Escalate legal interpretation to the client’s counsel or compliance owner.
- Record coverage. Compare the intended training population with assigned learners. Keep the source and date of that population clear.
- Track completion. Preserve assignment details, completion status, relevant course information, and exceptions. Distinguish overdue training from training that was never assigned.
- Close gaps. Assign an owner, document follow-up, and record the resolution. Where the client declines action, preserve that decision without presenting it as legal clearance.
This process distinguishes service delivery from compliance judgment. It also gives the next account manager or client reviewer something more useful than an unexplained dashboard status.
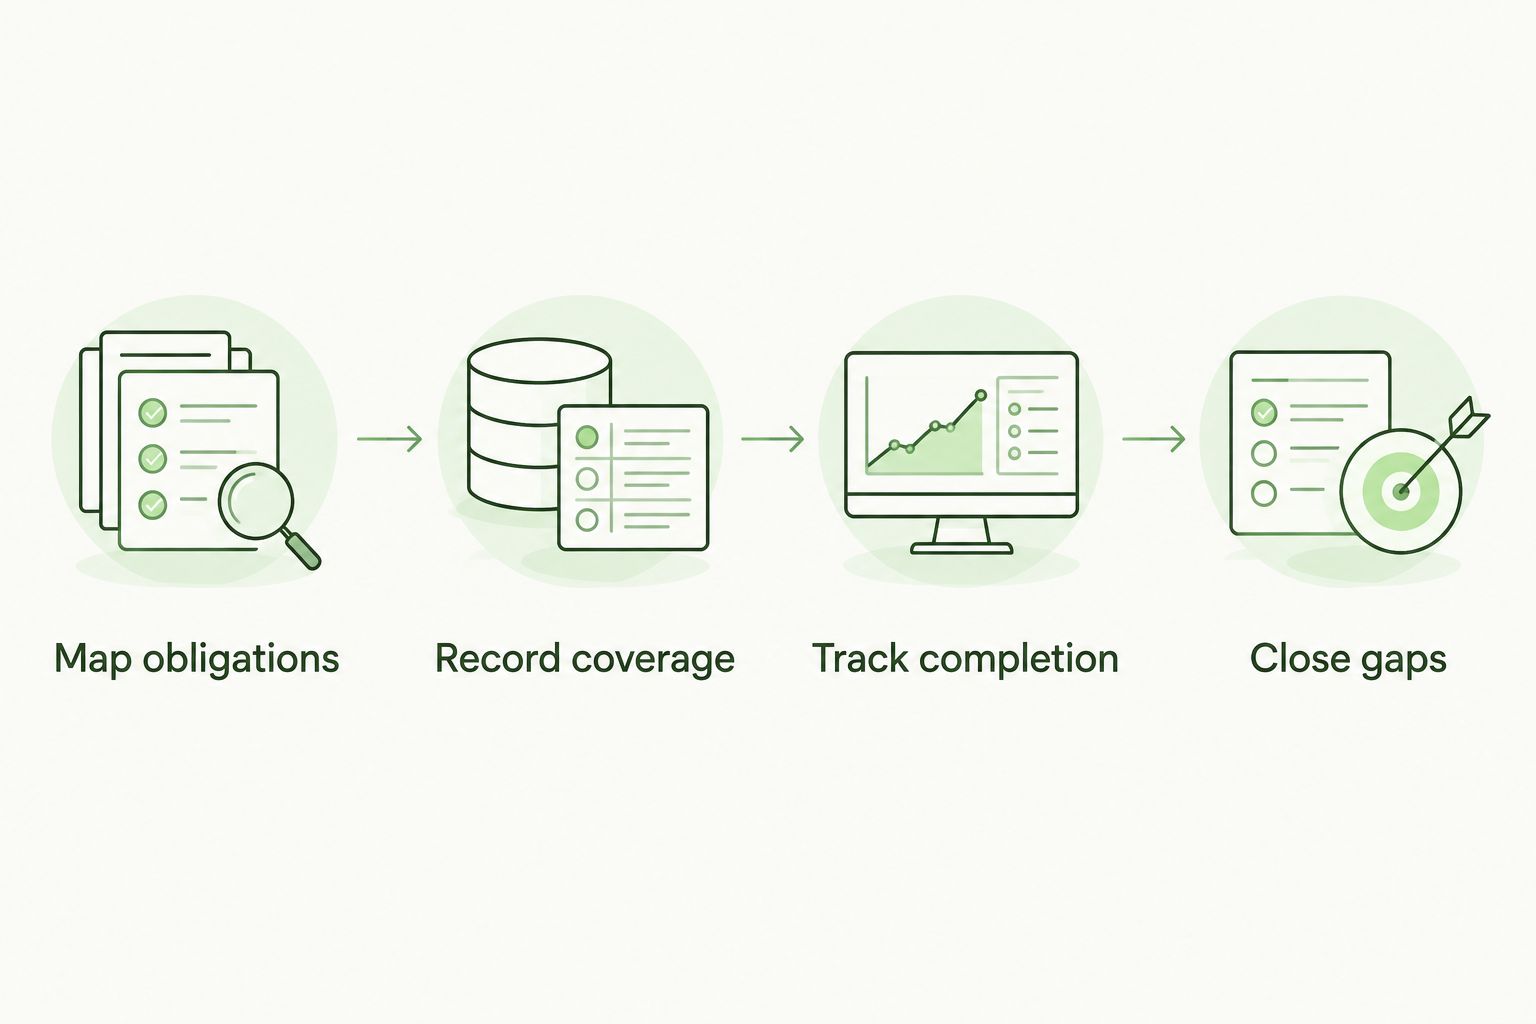
A training record should connect the requirement, covered population, completion status, and follow-up.
Does security awareness training software prevent fines?
No. Security awareness training software delivers part of a security program; it does not control every employee action, management decision, or legal requirement.
Defend Wise is best for MSPs that want white-label security awareness training without per-seat pricing. Its stated model combines a flat fee with unlimited seats, which removes per-seat charges from the platform’s pricing model.
That is an economic advantage, not a legal guarantee. Defend Wise security awareness training still needs to sit within a client-specific service scope, with clear responsibility for coverage, exceptions, and compliance decisions.
When evaluating the platform, verify the evidence and administrative functions your service requires. Do not assume that white-label delivery establishes a particular reporting export, retention setting, integration, or compliance outcome.
Can a completed course prove that a client is compliant?
No. A completed course proves completion of that recorded assignment, not compliance with an entire legal or contractual framework.
For a 2026 review, connect the record to the relevant workforce, assignment period, training content, and applicable requirement. Then assess any other controls that the requirement demands.
The practical benefit of completion evidence is specificity: you can show a recorded action. Its limitation is scope: the record cannot prove facts outside the action it documents.
FAQ
Is there a standard fine for missing security awareness training?
There is no universal fine for missing security awareness training. Financial exposure depends on the applicable law or contract, the actual failure, and the facts used to assess it.
Can an MSP be fined because a client did not finish training?
Client non-completion does not establish an automatic regulatory fine against the MSP. Assess the MSP’s own legal duties, contractual commitments, conduct, and responsibility for the relevant service.
Does HIPAA require security awareness training?
The HIPAA Security Rule requires a security awareness and training program for the workforce, including management. Review 45 CFR 164.308(a)(5) alongside the organization’s applicable obligations and documented implementation decisions.
How often does PCI DSS require security awareness training?
PCI DSS requires security awareness training upon hire and at least once every 12 months. Confirm applicable requirements and scope rather than treating the training schedule as a complete compliance program.
Does GDPR require every employee to complete an annual course?
GDPR does not prescribe a universal annual course schedule for every employee. Article 39 addresses relevant staff awareness and training within the data protection officer’s monitoring duties, while security measures must reflect applicable risks.
Does passing a SOC 2 examination remove regulatory exposure?
A SOC 2 examination does not remove regulatory exposure. Its scope and findings concern the examined controls and criteria, not blanket approval under every applicable law.
What should an MSP keep as evidence of security training?
An MSP should keep records that connect the agreed training obligation to assignments, covered learners, completion status, and follow-up. Define retention and access requirements with the client rather than assuming every record follows the same rule.
One last thing
Do not use a completed training dashboard as a substitute for a covered-workforce check. A completion percentage describes the population included in its calculation; it does not establish that everyone who needed training was included.
For your next 2026 review, compare the intended workforce with the assigned learner population before presenting completion results. Use Defend Wise to deliver the training service, and keep the client’s compliance assessment separate from the platform’s completion status.